
Sharp share drop and scope of the investigation
ASOS cyber incident sent the company’s shares down by about 10% in London on Tuesday. The company said it is investigating unauthorized activity on third-party platforms after unauthorized notifications were sent to app users. For the retailer, which serves about 17 million customers a year across more than 150 markets, the development is being closely watched for its reputational and market impact.
ASOS said some basic personal information may have been accessed, but it does not believe payment card data or account passwords were affected. The company also said its website and app are working normally, and customers can continue shopping.
How the alert spread and which systems are under review
It is not yet clear how many users received the notification sent on Tuesday morning. However, Google Play data shows the ASOS app has been downloaded more than 10 million times on Android devices; some users in Australia, France, Sweden and the Republic of Ireland were also reported to have received the same message.
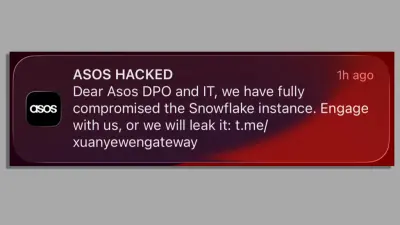
The message told attackers to contact the company’s data protection and IT teams, claimed that a Snowflake environment had been fully compromised, and included a link to a Telegram channel. Cybersecurity experts note that being able to send push notifications to app users would require access to a notification system separate from Snowflake, raising the possibility that the incident may not be limited to a single platform.
Initial assessments by institutions
Snowflake said in its ongoing review that it has not identified a breach on its platform so far. According to the BBC, the UK National Cyber Security Centre offered support to ASOS; the company also said it is working with internal and external experts, as well as the relevant authorities.
Key risks for customers and investors
ASOS said on Tuesday that it moved immediately to restrict access to notification platforms. Even so, at the time of publication, the company had not yet reported a breach to the UK data watchdog, the Information Commissioner’s Office (ICO).
Experts say the aim of the attack may be to increase pressure on the company rather than directly target customers. Still, the incident poses risks to the retailer’s revenue outlook and brand value because of data leak concerns, possible fraud attempts and weaker customer trust.
Key precautions for users
- Do not click on links included in the notification
- Follow updates only through the company’s official channels
- Be cautious about refund or support offers made by email, SMS or phone calls
- Use different passwords across services and enable two-factor authentication
Comments (0)
No comments yet. Be the first to comment.
Write a Comment
Yorum yazmak için giriş yapın. Üyelik ücretsiz; yorumunuz editör onayından sonra yayımlanır.